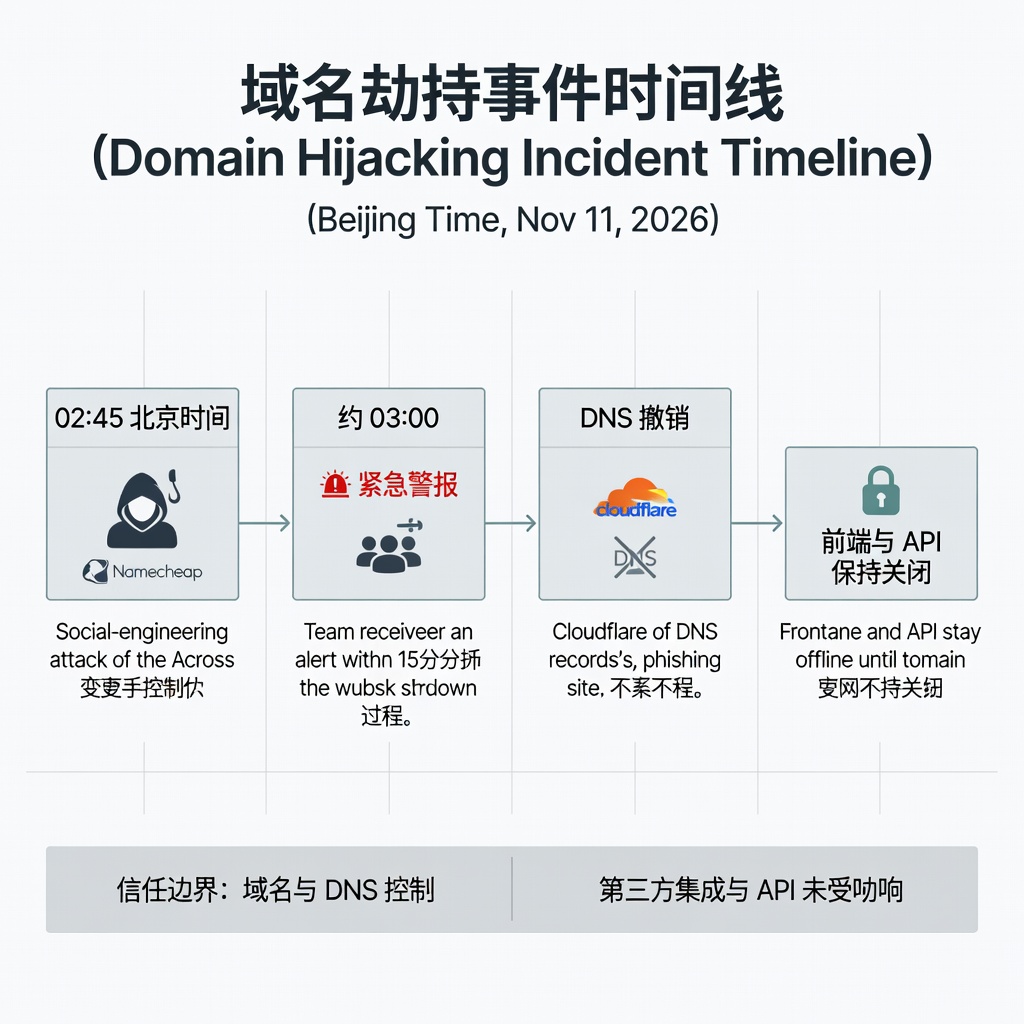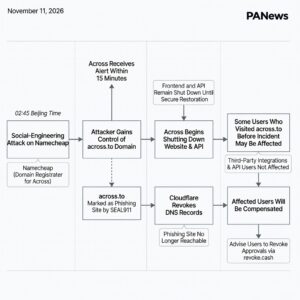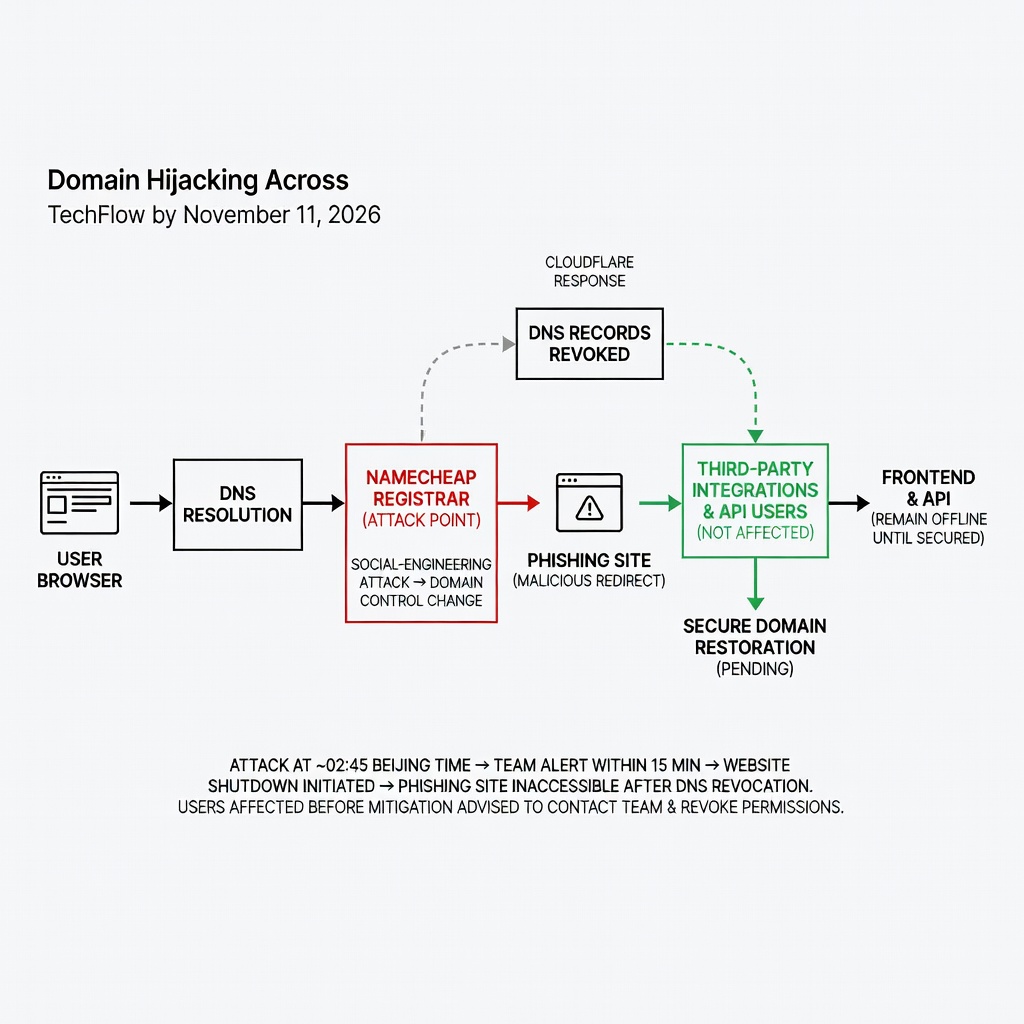
In a report published November 11, 2026, TechFlow relayed an official announcement from the cross-chain protocol Across: attackers gained control of the Across domain after a social-engineering attack on its registrar, Namecheap.
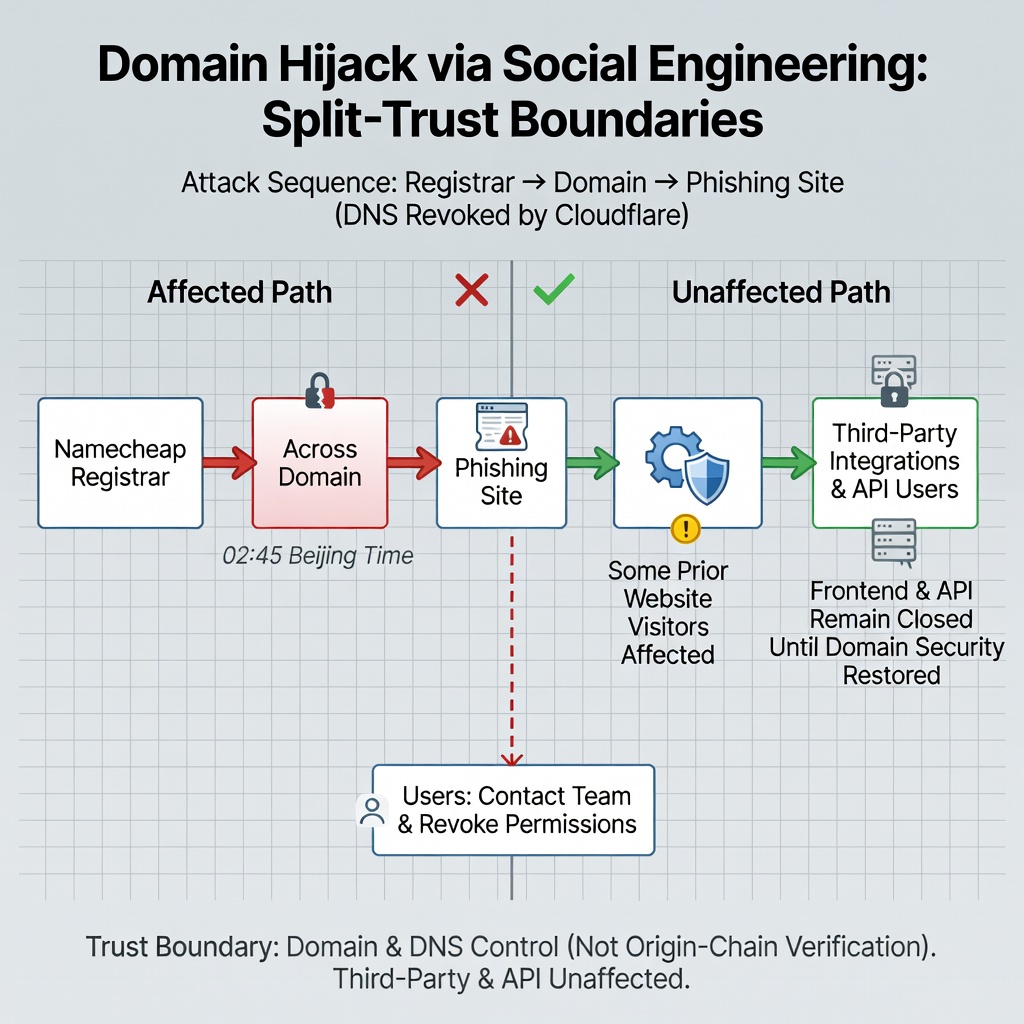
Across said the takeover occurred around 02:45 Beijing time. The team received an alert within 15 minutes and began shutting the website down.
Cloudflare then revoked the domain’s DNS records. Across said the phishing site could no longer be accessed. Some users who had visited the site before that point may have been affected. Third-party integrations and API users were not affected, the project said.
Users who believe they were affected were advised to contact the team and revoke the attacker’s permissions. Across said its frontend and API would remain closed until domain security was restored.
The sequence described runs through the registrar and the public domain name, not from an origin-chain lock through verification to a destination-chain outcome. Namecheap is the point where control of the Across domain changed hands, after which a phishing site stood in until Cloudflare removed the DNS records. The announcement does not describe assets being locked, burned, or minted, or a message being passed between chains. The trust boundary it names is domain and DNS control. Across separated that path from third-party integrations and API access, which it said were not affected, while keeping its own frontend and API offline until the domain was secured.
Source: TechFlow, November 11, 2026, 06:26 UTC+8.