PANews reported on November 11, 2026, at 06:24 (UTC+8), that the cross-chain protocol Across had posted on X about a domain incident earlier that morning. The report describes a registrar and DNS handoff, not a bridge transfer, lock, burn, mint, or cross-chain message.
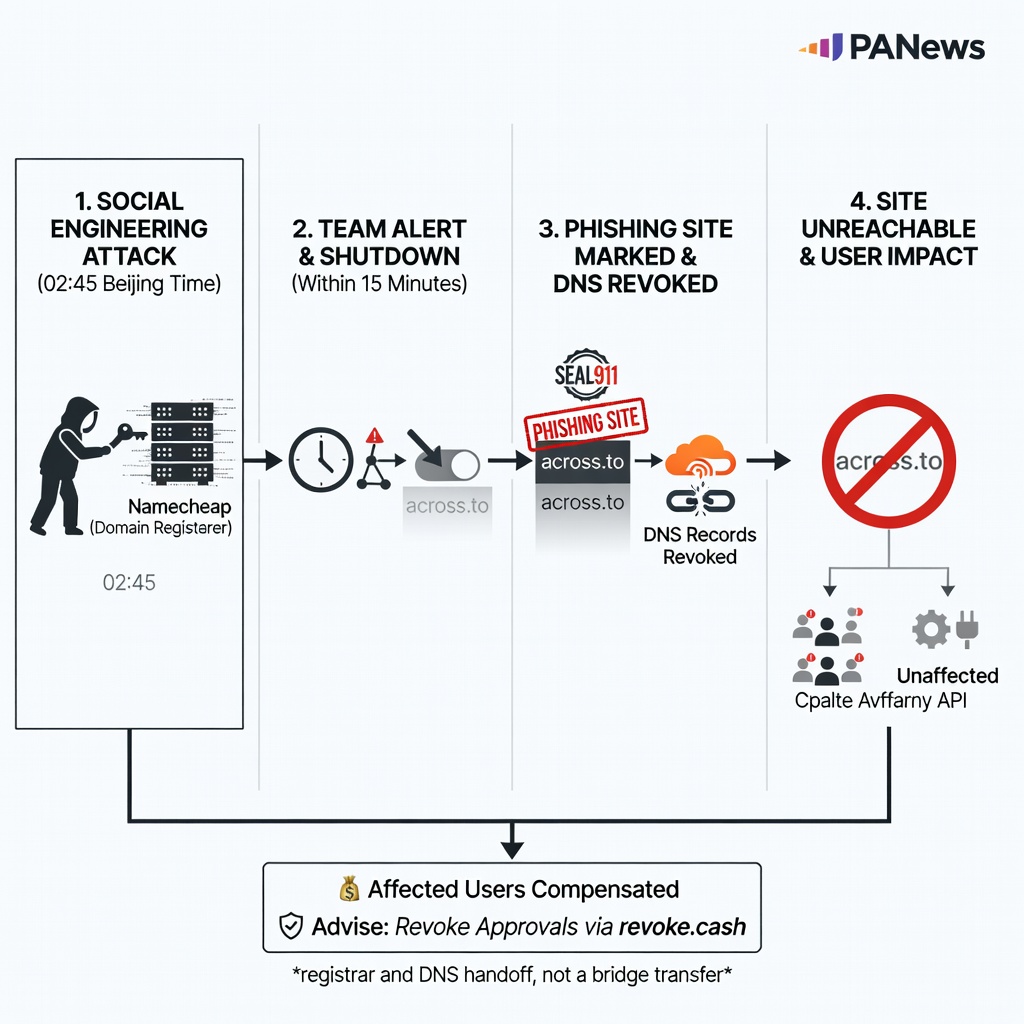
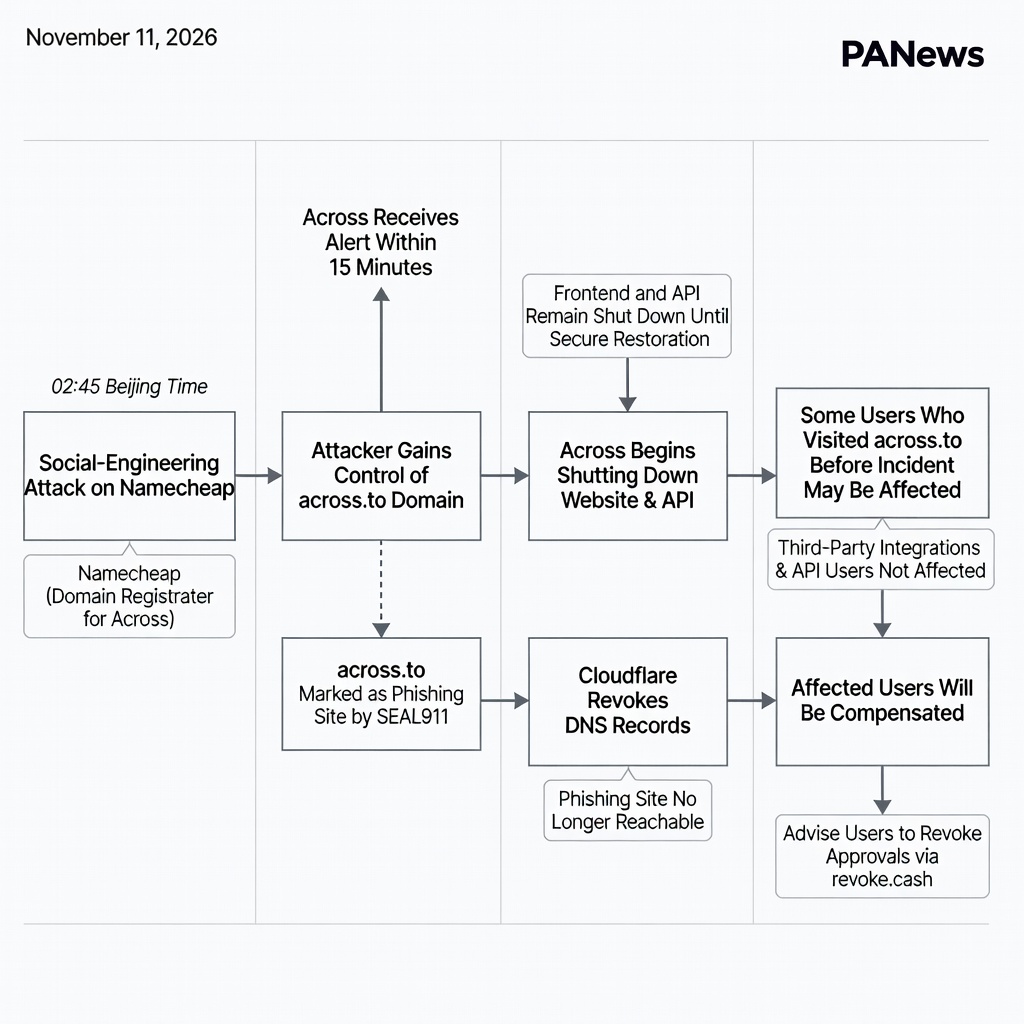
Across said that around 02:45 Beijing time on November 11, its domain registrar, Namecheap, was subjected to a social-engineering attack. Across said that attack let the attacker take control of the Across domain. The team said it received an alert within 15 minutes and began shutting the website down.
PANews reported that across.to had been marked as a phishing site by SEAL911. Cloudflare then revoked the domain’s DNS records, and the phishing site could no longer be reached.
Across said some users who had visited across.to before that point may have been affected. It said third-party integrations and API users were not affected. Across said all affected users will be compensated and advised users to revoke related approvals through revoke.cash.
Until the domain is securely restored, Across said its frontend and API will remain shut down. The stated trust boundary in the report is control of the domain at the registrar and in DNS. The notice does not describe any change to how Across verifies messages or handles assets on a destination chain.
Original report: PANews